


Portfolio-wide standard operating model with a single system of record to measure, track, and continuously improve cyber resilience across portfolio companies- from pre-acquisition to exit readiness.
The Cybersecurity Hub
A Unified System of Record for Portfolio-wide Cyber Resilience
Explore The Program

Trusted by industry leaders around the globe


Standardization
Use Cye to document, measure, and track cyber maturity and risk across your portfolio throughout the holding period.
Centralized Oversight
Provide operating teams visibility into portfolio cyber risk and maturity, enabling comparative insights and action.
System of Record
Create a central repository for portfolio cybersecurity status, enabling continuous governance and reporting across companies.
This Is Cye
Cyber Maturity Assessment
Standardized NIST‑CSF maturity scoring across the portfolio.
Cybersecurity Uplift
Turn findings into uplift plans tied to value and exit readiness.
Financial Exposure
Financially quantify cyber risk to prioritize portfolio investments.
Reporting
One system of record for portfolio governance and quarterly reporting.


Portfolio-Wide Solutions
Maturity Management
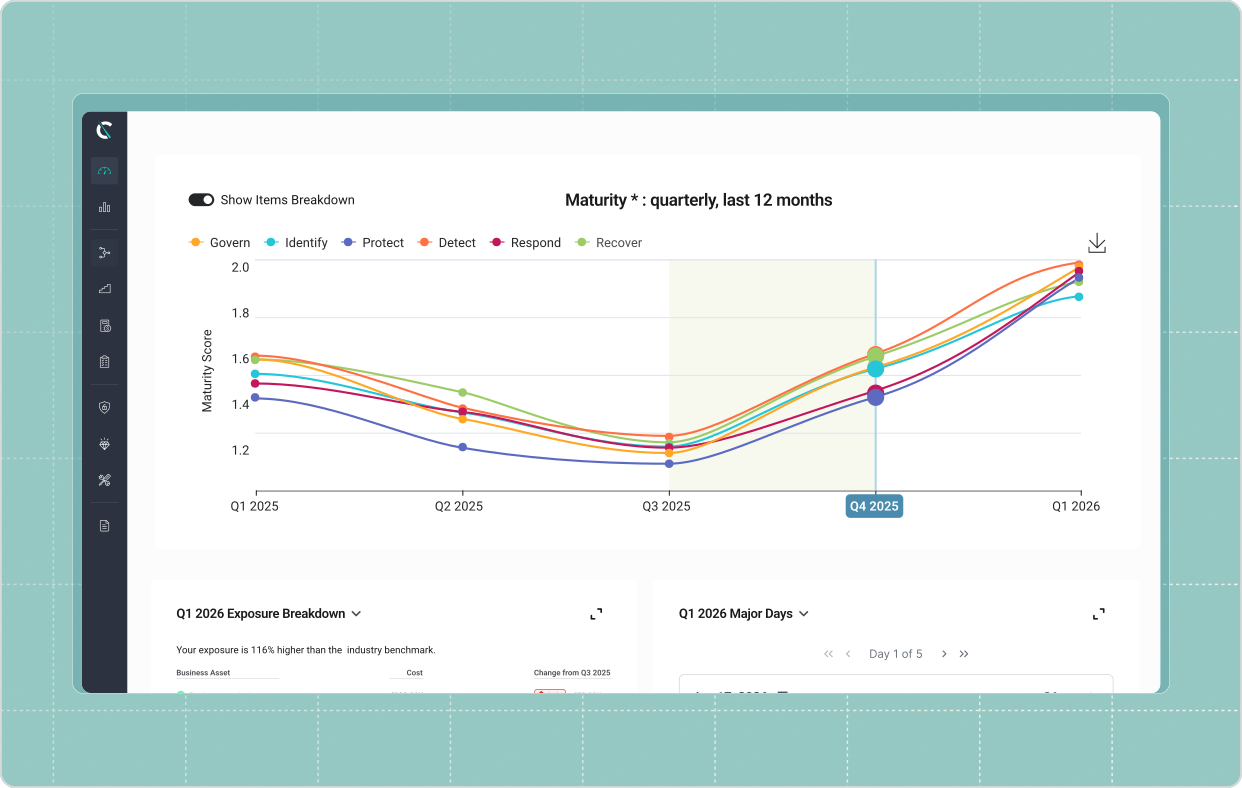
Gain a clear view of cybersecurity maturity with Cye’s AI-led mapping across the six NIST CSF functions. Measure maturity by function and subcategory, benchmark against peers, and define targeted remediation plans to close gaps.
Cye’s Platform
Our Platform
Gain a clear view of your cybersecurity maturity with Cye’s AI-led mapping across the six NIST CSF functions. Continuously monitor your cyber maturity by function and subcategory, set maturity targets with remediation plans, and benchmark against industry peers.

- 500+Customers served
- 96%of customers' business-critical attack routes are blocked within six months.
- 88%reduction in remediation time following a cyber incident.
- 87%of customers improve ROI on their security budget.
Built On Proven Security Standards
- ISO/IEC 27001:2022
- SOC 2 Type II

- GDPR

- CREST

- ISO/IEC 42001:2023
Need more information?
Frequently Asked Questions
Cye can support your portfolio throughout the investment lifecycle—from pre-deal scouting and due diligence through post-acquisition improvement, ongoing exposure management, and exit readiness.
Before acquisition, Cye helps you identify cyber risks that could affect valuation, deal terms, or the decision to proceed.
In the first 90 days after close, Cye establishes a cybersecurity baseline and prioritizes the actions needed to address critical gaps.
Throughout the hold period, Cye provides continuous visibility into cyber exposure and maturity, helping portfolio companies prioritize and reduce risk while giving the PE firm a portfolio-wide view of progress.
Before exit, Cye helps demonstrate measurable improvement in cyber maturity and exposure, providing evidence of progress to prospective buyers.
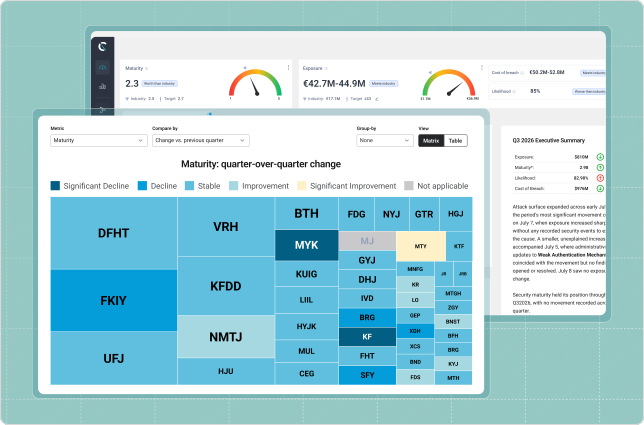
At the private equity firm level, Cye provides a centralized, portfolio-wide view of cyber maturity and exposure. Benchmark holdings, identify outliers, drill down into individual companies and track progress over time, with reporting for the board and investment committee.
At the portfolio company level, Cye offers Maturity Management and Exposure Management:
Maturity Management helps companies establish and continuously improve their cybersecurity program — assessing maturity against NIST CSF 2.0, identifying gaps, prioritizing improvements and tracking progress.
Learn more about Maturity Management
Exposure Management identifies and prioritizes cyber exposure based on exploitability and business impact, using attack-path analysis to drive targeted mitigation.
Learn more about Exposure Management
Together, these solutions create a consistent view from portfolio company to PE firm, giving investment teams the visibility to understand risk, prioritize action and measure progress across the portfolio.
You can start with the portfolio companies where cybersecurity support is most needed and expand over time. Each portfolio company can enroll in either Maturity Management or Exposure Management.
As new acquisitions are added, they can be brought into the same portfolio structure and reporting framework, giving the PE firm a consistent view.
Cye provides a consistent framework for comparing cyber maturity and exposure across the portfolio, while accounting for each company’s unique environment and risk profile.
Maturity is measured against NIST CSF 2.0, while exposure is assessed based on vulnerabilities, attack paths, critical assets and business impact. Cye can also weight exposure by each company’s equity value, helping the PE firm see where the greatest investment is at risk.
This enables PE firms to benchmark holdings, identify outliers and prioritize action without applying a one-size-fits-all approach. Cye AI can also compare companies and quickly surface differences in maturity, exposure and financial impact.
Progress is continuously visible in the platform from the baseline established during the first 90 days, giving you an ongoing view of how cyber maturity and exposure are changing across each portfolio company.
You can track improvement over time and measure the impact of remediation rather than waiting for an annual assessment. Across Cye's customers, 96% of business-critical attack paths are blocked within six months of starting.
Due diligence findings are stored in a temporary platform instance for the deal team to review. If the deal does not close, or closes without further engagement, access is closed and the data is cleaned up at the end of the diligence process. Ongoing platform access begins when a company enters the hold-period program.